Malware Analysis Report
Introduction
Key points:
Nature: Confirmed Trojan (Kinsuky family) with high malicious confidence.
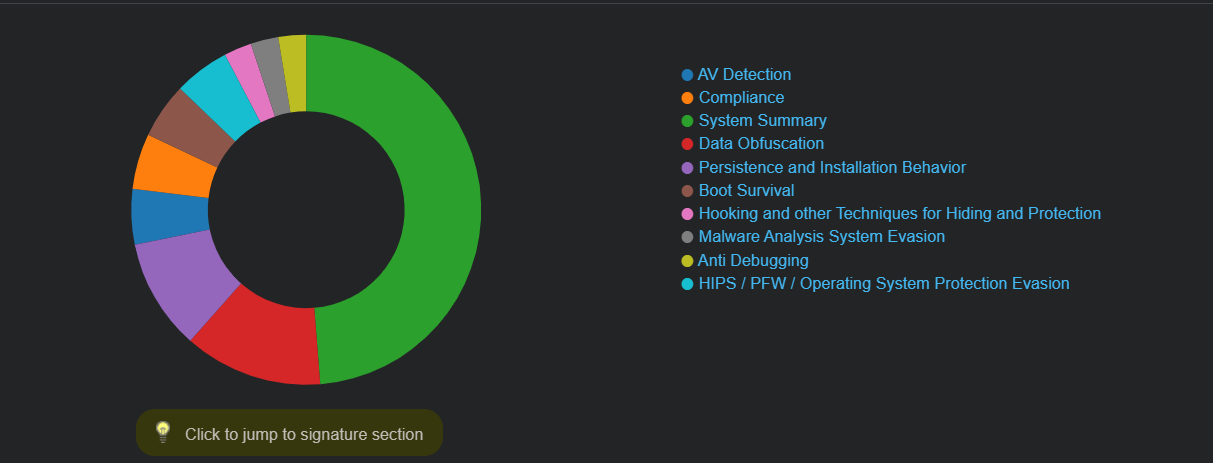
Evasion: Uses obfuscation and techniques to detect debug environments (sandbox evasion).
Persistence: Establishes a foothold on the system.
Activity: Drops the executable
svc.host.exeand attempts Command and Control (C2) communication with domains likea1668.dcc.akamai.netand several IPs.Risk: High risk of system compromise, data theft, and further malware deployment
1. Executive Summary
The sample 95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485 appears to be a Trojan with high confidence, specifically identified by multiple vendors as belonging to the Kinsuky family. It exhibits evasive behavior, including detecting a debug environment and using obfuscation and persistence mechanisms. The file is a Windows DLL named osinfo.dll.exe (though the file type is listed as DLL and the name as osinfo.dll and osinfo.db in other sections, the primary analysis shows a DLL/EXE).
Top IOCs:-
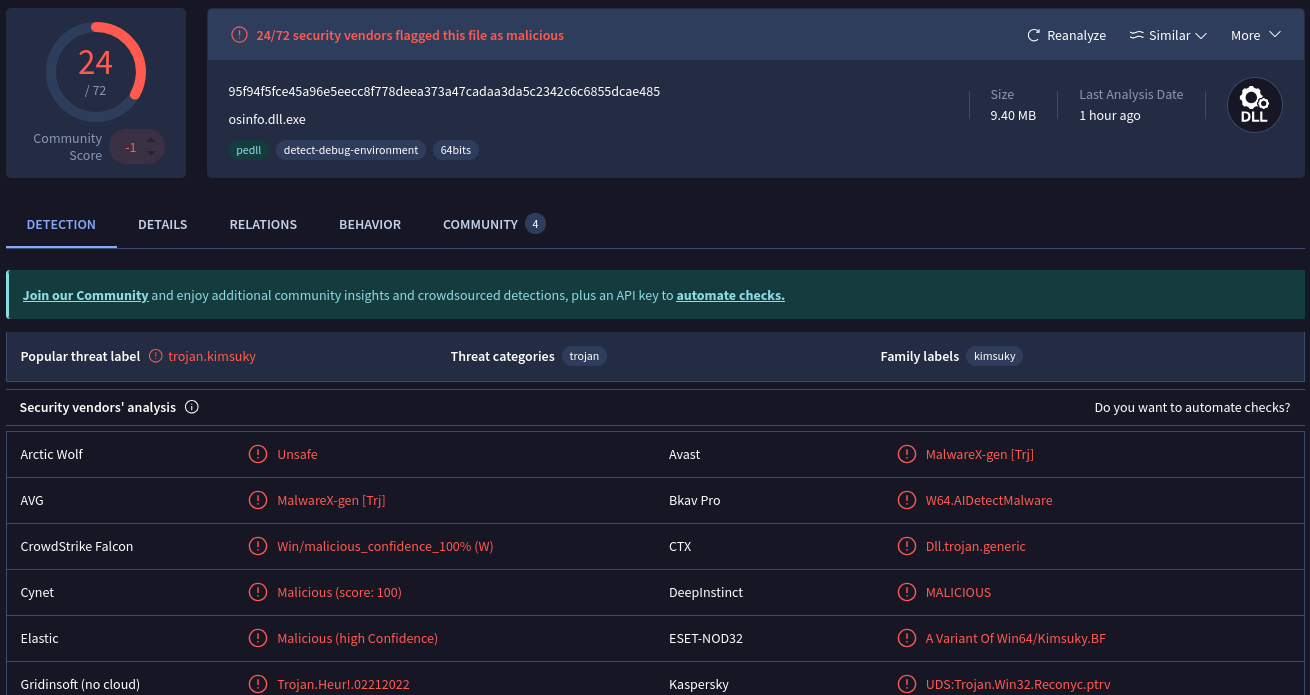
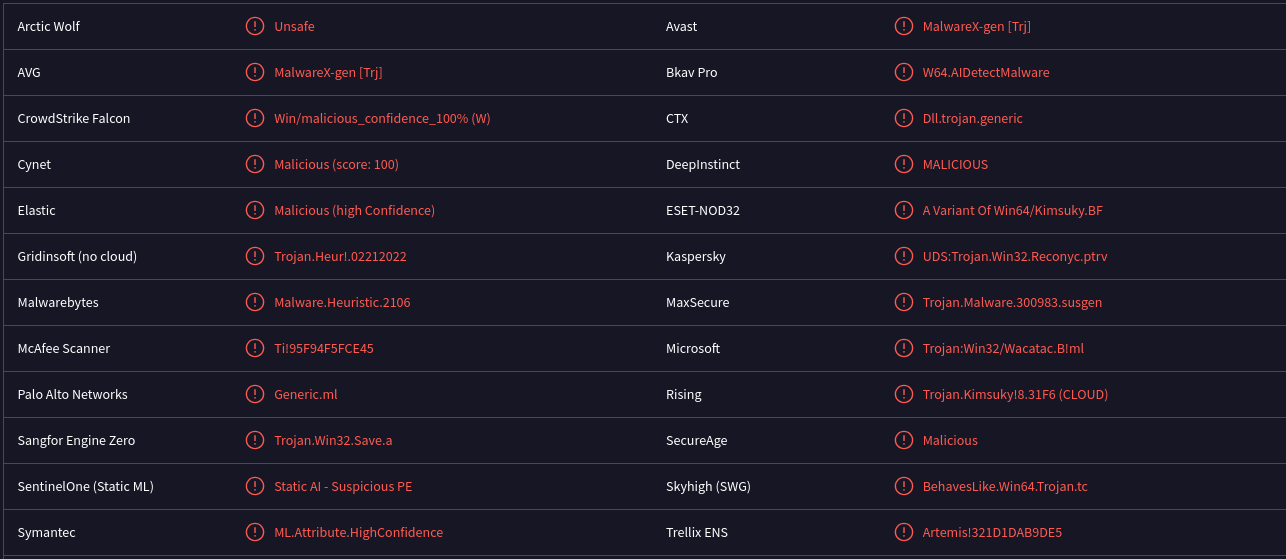
SHA-256:
95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485Domain:
a1668.dcc.akamai.netIP Address:
1.1.1.1Threat Family: Kinsuky
MITRE ATT&CK: T1059.001 (PowerShell), T1547.001 (Registry Run Keys), T1027 (Obfuscated Files).
2. Sample Metadata
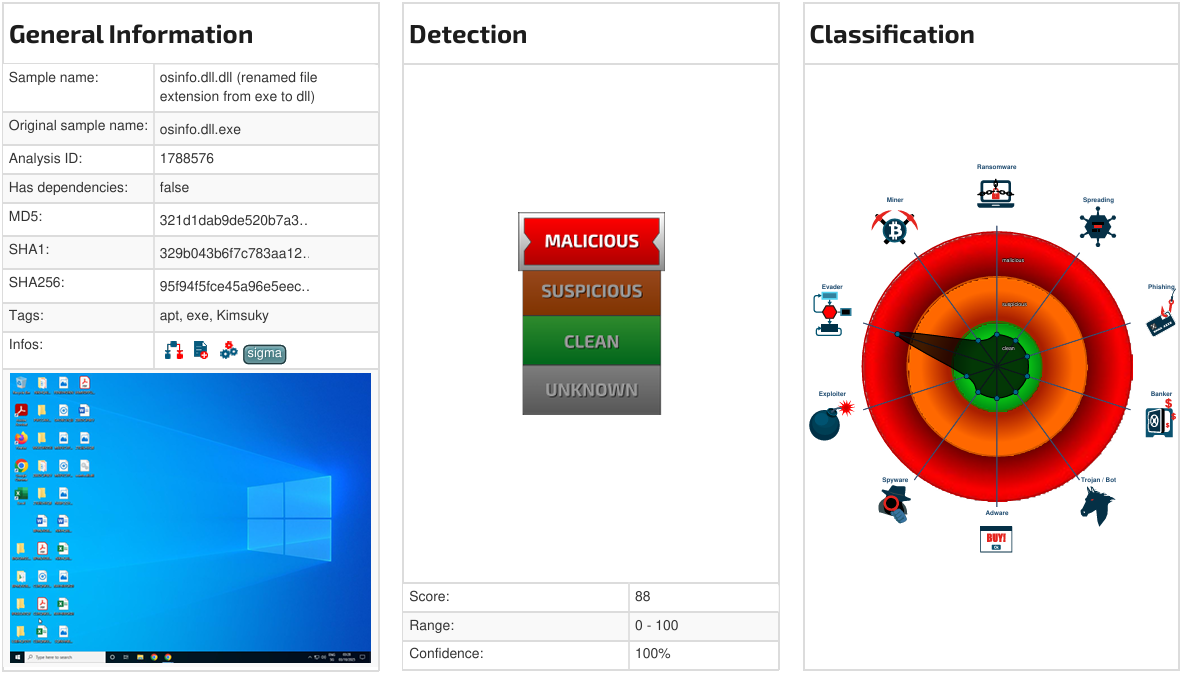
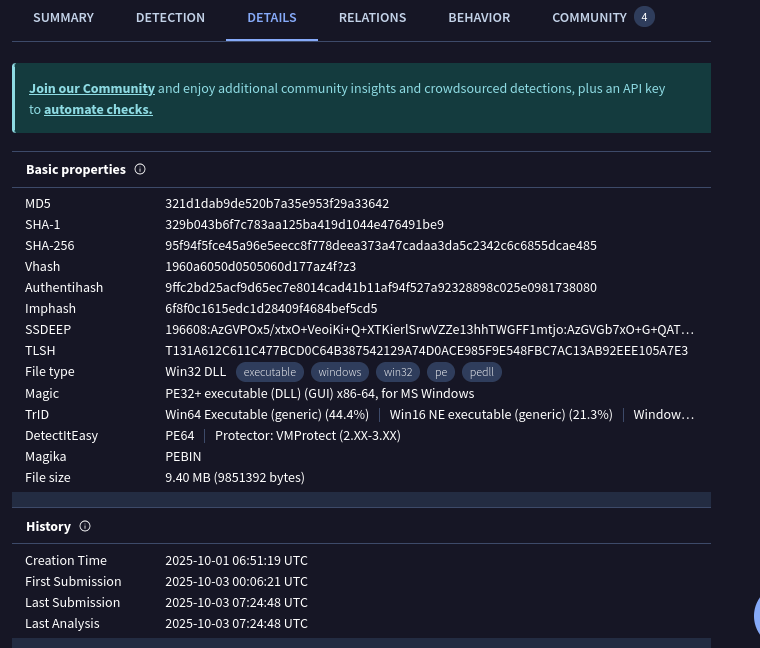
Field | Value |
SHA-256 |
|
MD5 |
|
SHA-1 |
|
File Name(s) |
|
File Type | DLL, Win32 EXE (GUI) x64 |
File Size | 9.40 MB (9851392 bytes) |
First Submission | 2025-10-03 00:08:21 UTC |
Last Analysis Date | 2025-10-03 07:24:40 UTC |
Community Score | 24 / 72 (Malicious) |
Threat Family | Kinsuky |
3. Static Analysis Results
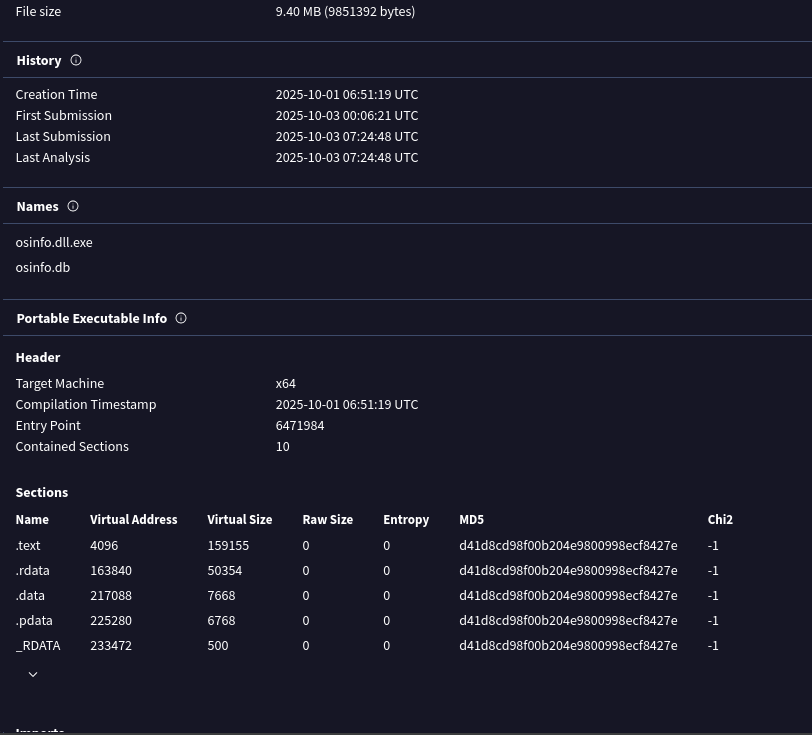
PE Headers (Extracted from Details)
Field | Value |
Magic | PE32+ executable (DLL) (GUI) x64, for MS Windows |
TrID | Win64 Executable (generic) (44.4%), Win16 NE executable (generic) (21.3%) |
Target Machine | x64 |
Compilation Timestamp | 2025-10-01 06:51:19 UTC |
Entry Point |
|
Packed/Protected | Yes (VMProtect: VMPROTECT (2.XX-3.XX)) |
Imports/Exports | Not explicitly shown, but indicated by DLL file type |
Embedded Strings of Interest
Behavior Tags:
pedll,detect-debug-environment,64bits,obfuscated,persistenceDropped Files:
svc.host.exe(Win32 EXE, dropped on 2025-09-23 and 2025-09-07)File Name (other):
3b133c0362ba40061f9dca2d994ff4c2c556940803b44f70fb730508f7f5305064(File entry with no type, possibly a dropped file name)
YARA Rule (Minimum Viable)
rule Win_Malware_Kinsuky_95F94F {
    meta:
        author = "Analyst"
        description = "Detects Kinsuky Trojan sample 95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485"
        family = "Kinsuky"
        hash = "95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485"
        date = "2025-10-03"
    strings:
        $sha256 = "95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485" ascii wide
        $mz = "MZ" at 0
        $timestamp = { 19 51 01 00 64 0a c4 01 } // Hex for 2025-10-01 06:51:19 UTC
    condition:
        uint16(0) == 0x5a4d and $sha256 or $timestamp
}
4. Dynamic Analysis Results
Command-line behavior, Child Processes, File System Modifications
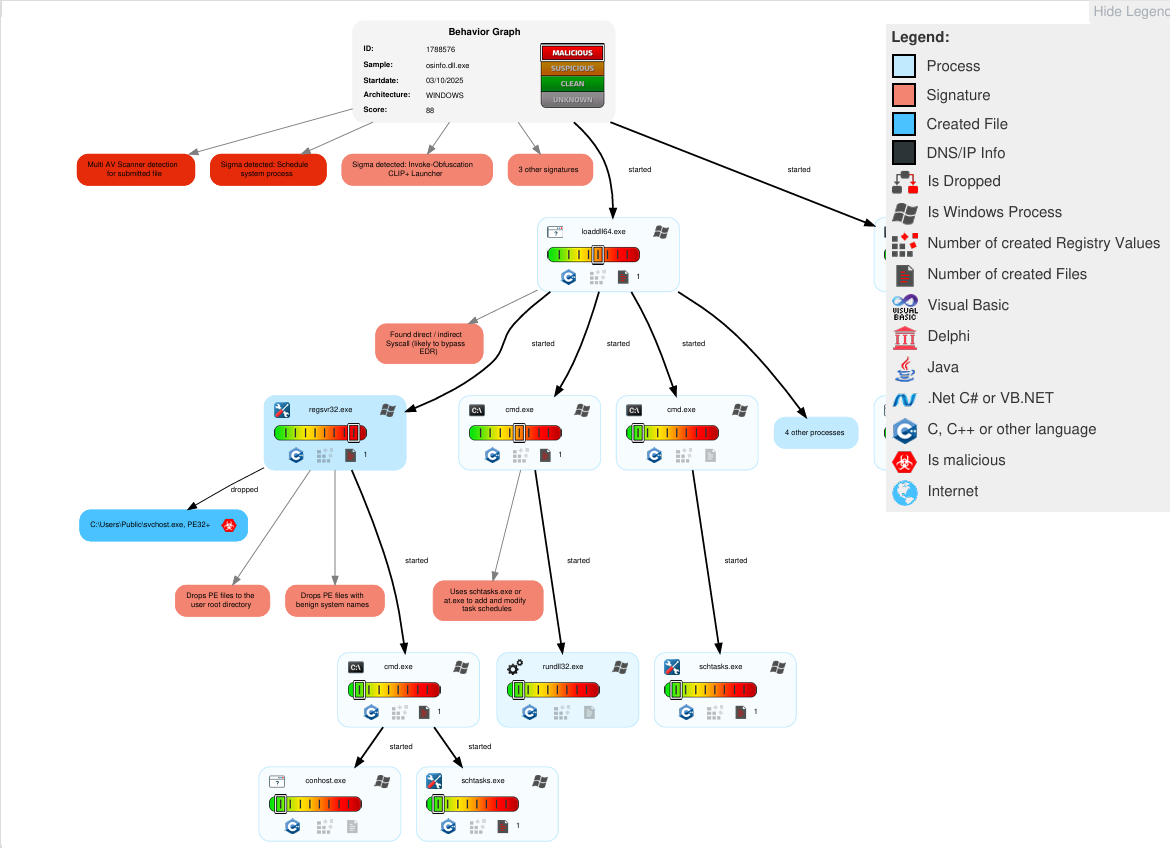
Dropped Files: 3 total dropped files observed, including a known malicious file,
svc.host.exe(Win32 EXE).Bundled Files: 4 bundled files observed, including an XML file (
.rsrc/MANIFEST2).File System Modifications: Specific paths not shown, but likely include creating the dropped files.
Mutexes & Registry Keys
Mutexes: Not explicitly shown in screenshots.
Registry Keys (Windows): Persistence mechanism is tagged, highly suggesting modifications to Registry Run Keys (e.g.,
HKCU\Software\Microsoft\Windows\CurrentVersion\Run) or similar methods.
Network Behavior
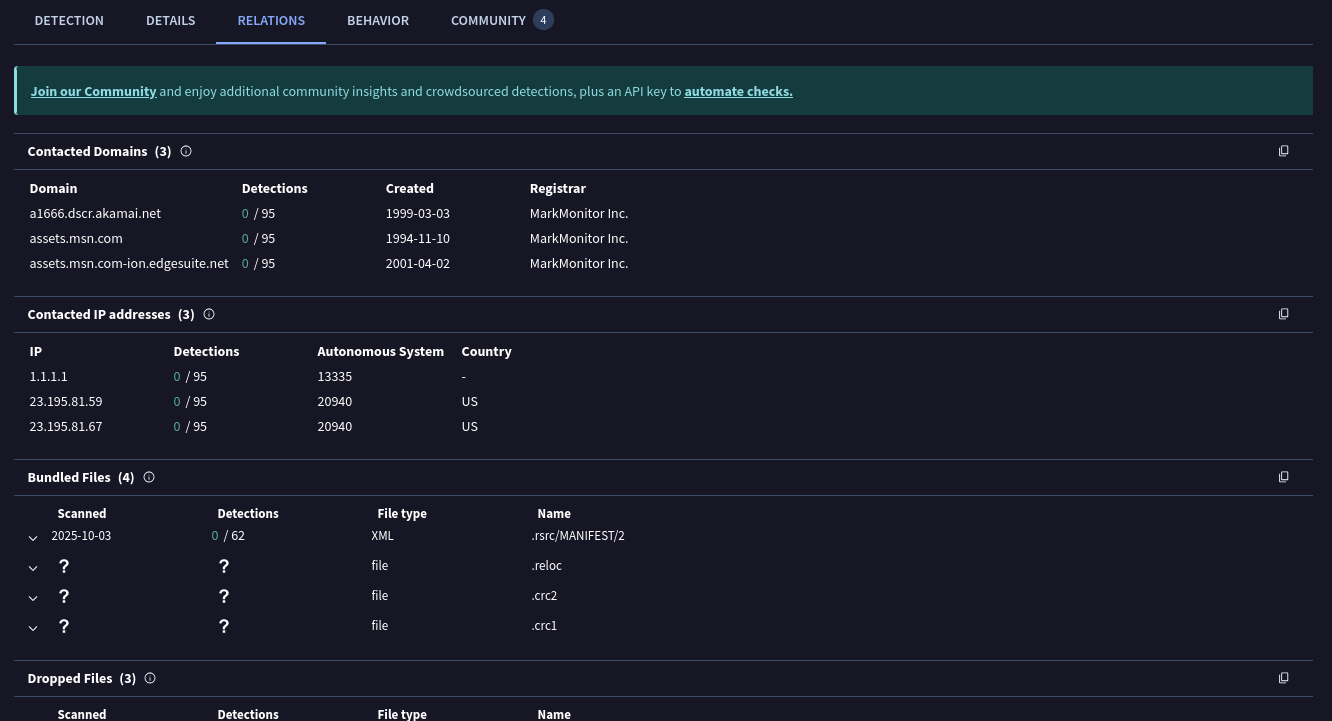
Type | Value | Detections |
Contacted Domain (FQDN) | 0 / 95 | |
Contacted Domain (FQDN) | 0 / 95 | |
Contacted Domain (FQDN) | 0 / 95 | |
Contacted IP |
| 0 / 95 |
Contacted IP |
| 0 / 95 |
Contacted IP |
| 0 / 95 |
Network Comms Summary | 3 DNS, 1 IP | - |
C2 Ports/Protocol | Not explicitly shown, but likely HTTP/S on standard ports. | - |
Persistence Mechanisms Observed
- Behavior tag:
persistence. This typically involves setting a Run key, creating a service, or adding a scheduled task.
- Behavior tag:
5. IOC Collection
File IOCs:-
| Hash Type | Value |
| sha256 | 95f94f5fce45a96e5eecc8f778deea373a47cadaa3da5c2342c6c6855dcae485 |
| md5 | 32d1d0abddc520b7a35e93f729a3f642 |
| sha1 | 329b04b2b6f7c783aa123a419d1044e1f76491b9 |
| ssdeep | 196608:AzGvPoXiS/vto+VEouXkiG+qXTkflE/Sfw/rWvZZoL3hTHWGGf1fmtjo:AzGvGB/Tx+Q+qXATNDSNwVLURhJ/F6 |
Network IOCs:-
Type | Value | ASN | Country |
Domain | - | - | |
Domain | - | - | |
Domain | - | - | |
IP Address |
| 13335 | - |
IP Address |
| 20940 | US |
IP Address |
| 20940 | US |
Host IOCs:-
Type | Value | Notes |
File Name |
| Main sample name |
File Name |
| Dropped file, potential next stage |
Registry Key | Implied persistence mechanism | Check common run keys/startup folders |
6. MITRE ATT&CK Mapping
Tactic | Technique ID | Technique Name | Evidence |
Execution | T1059.001 | Command and Scripting Interpreter: PowerShell | 2 Detections (Implied by sandbox behavior) |
Persistence | TA0003 | Persistence | Behavior Tag: |
Defense Evasion | TA0005 | Defense Evasion | Behavior Tag: |
Defense Evasion | T1027 | Obfuscated Files or Information | Behavior Tag: |
Defense Evasion | T1497.001 | Virtualization/Sandbox Evasion: System Checks | Behavior Tag: |
Privilege Escalation | TA0004 | Privilege Escalation | Explicitly tagged in MITRE ATT&CK section |
Command and Control | TA0011 | Command and Control | Contacted Domains/IPs (3 DNS, 1 IP) |
7. Impact & Affected Systems
OS: Windows (Win32 DLL/EXE, x64 architecture).
Likely Privilege: Requires user-level execution to install persistence, but may attempt to escalate privileges (TA0004 tag).
Lateral Movement Potential: Possible, especially if
svc.host.exeis a worm or uses file share/network logon capabilities.Data Exfiltration Risk: High, given its Trojan classification (often a precursor to data theft or further compromise).
8. Mitigation & Detection Recommendations
Type | Rule/Indicator | Recommendation |
Network (Block) | FQDN: | Block at firewall/proxy. |
Network (Block) | IP: | Block at firewall/IPS. |
Network (Block) | IP: | Note: This is a public DNS resolver. Block only if C2 is confirmed to use it directly, or monitor for unusual traffic to it. |
EDR (Hunting) | Search for files matching SHA-256 hash or the | High-priority investigation. |
EDR (Hunting) | Look for newly created files named | High-priority investigation. |
EDR (Detection) | Sigma Query: Alert on child processes spawning from | Focus on T1027 and T1497.001. |
EDR (Detection) | YARA Rule: Deploy the provided YARA rule for endpoint scanning. | Immediate detection capability. |
9. Repro Steps & Evidence
Sandbox Link: Not provided in the screenshots.
Screenshots/Evidence: See attached images (
image_8bc6f3.png,image_8bc791.png, etc.) for dynamic analysis overview, detection details, relations, and MITRE mapping.Evidence of Malware Evasion:
image_8bca56.png(Zenbox & Dr.Web vxCube flag as MALWARE EVADER).Evidence of Dropped Files:
image_8bc6f3.png(svc.host.exedropped files).Evidence of C2:
image_8bc69e.png(Contacted Domains/IPs).
10. References
Public Reports: None explicitly used, but search for "Kinsuky Trojan" or the SHA-256 for public analysis.
VT Link: URL corresponding to the SHA-256 hash on VirusTotal or a similar platform.
MISP/OpenCTI: References to other internal/external intelligence on the Kinsuky family.